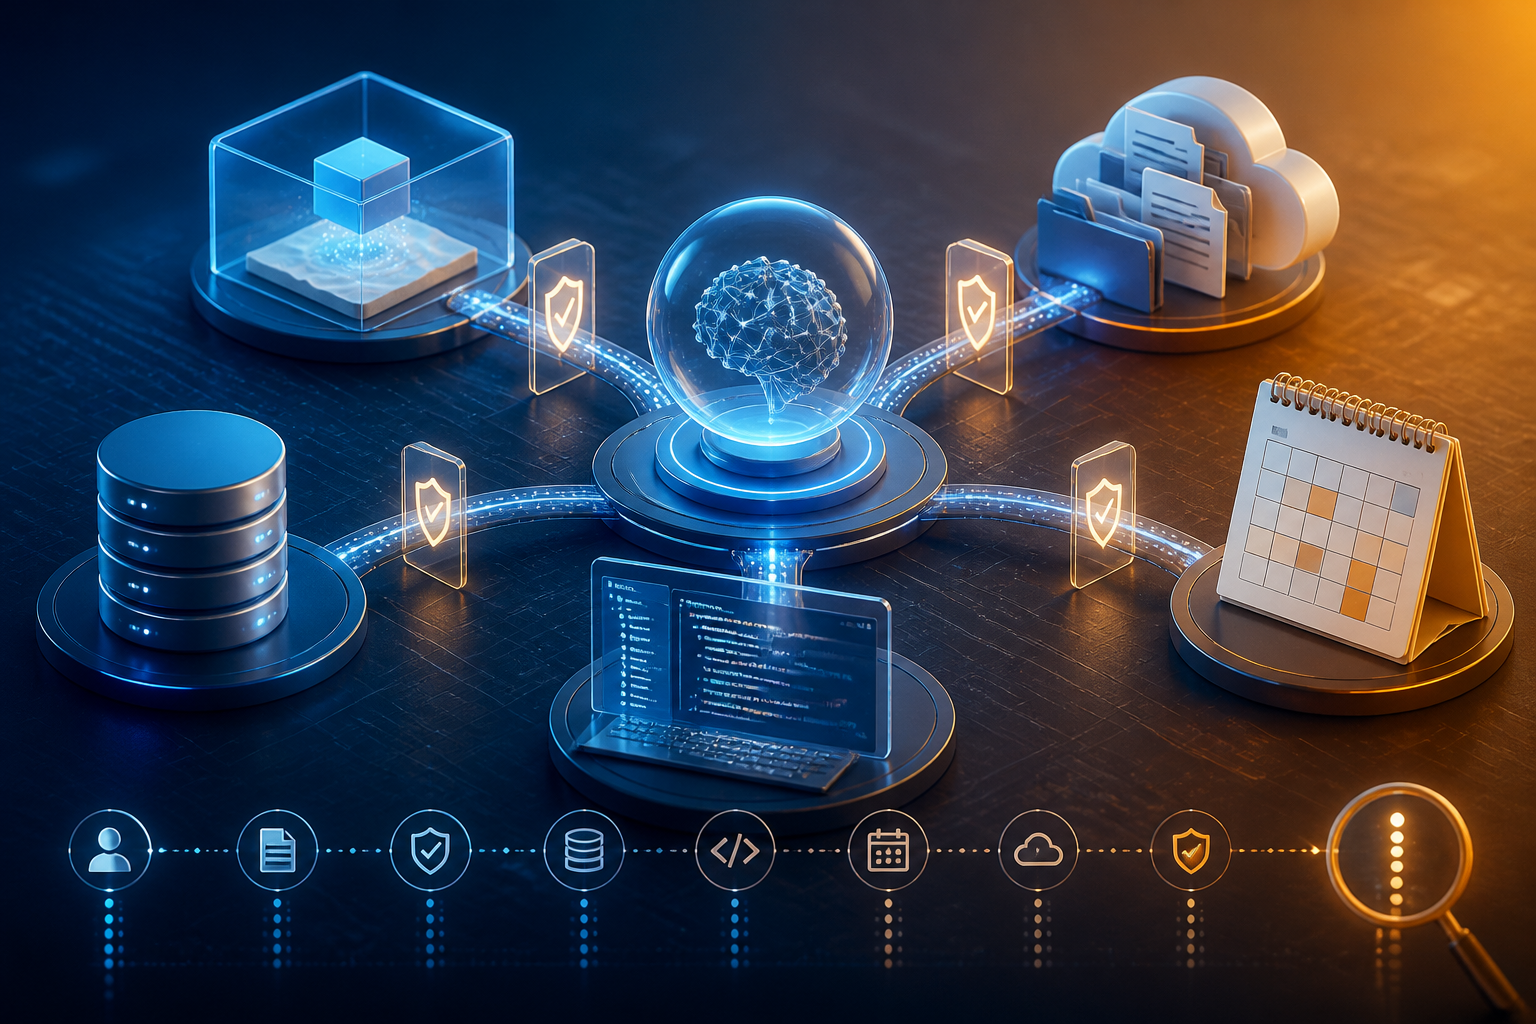
AI agents are beginning to move from merely answering questions to performing a series of tasks. They can read documents, execute code, use specific tools, access company systems, and return organized results.
This change is evident from several recent developments. OpenAI introduced the Agents API to build and run long-term agents with support for files, code, subagents, and managed work environments. Google Cloud announced the Gemini agent designed to plan tasks, use connectors and tools, and operate in environments like email, documents, calendars, and business systems. On the other hand, Anthropic continues to expand the agent connection ecosystem through SDKs, MCP servers, and integrations for enterprise work.
However, there is one important lesson from this direction of development: smarter models are not the only requirement for AI agents to be useful. In practice, a great agent without access to the right data is like a smart employee who is not given documents, room keys, or work procedures.
From Answering Ability to Action Capability
Traditional chatbots typically operate in a single loop: the user asks, the system answers. AI agents work in multiple steps. They can break down goals into smaller tasks, select the necessary tools, check interim results, and adjust plans if they encounter obstacles.
For example, the request “prepare a summary of this month’s sales report” could mean:
- Fetching data from spreadsheets or sales systems.
- Cleaning up empty or duplicate data.
- Calculating changes compared to the previous month.
- Finding products with the largest decline.
- Creating a summary for the manager.
- Saving the results to a document or sending them via email.
In this example, the quality of the answer is only part of the issue. The agent must also know which data sources are permissible, whether it can send emails, how to handle unreasonable numbers, and when to seek human approval.
Connectors Become the Most Important Part
Connectors are bridges that link agents with other services, such as cloud storage, CRM, calendars, databases, ticket systems, or development tools. Without connectors, agents can only provide suggestions. With connectors, they can start doing work.
This is why various AI providers now emphasize access to tools and systems, not just model capabilities. OpenAI explains that the Agents API is designed to perform tasks in a sandbox, using files and code, and coordinating subagents. Google Cloud describes the Gemini agent as a layer that can select models, use skills and tools, and connect to business systems. Anthropic also places connectivity as an essential part of agent capabilities through MCP and development tools.
This has implications for organizations and individual users. Deploying an AI agent is not just about selecting a model and turning on features. We need to map the data and actions that the agent can access. If all connections are granted at once, a small mistake can spread to many systems.
Sandbox: A Workspace Before Real-World Access
Sandbox is a limited environment where agents can read files, run code, or test actions without directly touching the production system. The concept is similar to providing a workspace and trial account before someone is given the keys to the main office.
Sandboxes are useful because agents can make mistakes in a relatively safe manner. They might choose the wrong command, create too many temporary files, or produce changes that do not align with instructions. If all processes occur in the production system, these mistakes could lead to data deletion, configuration changes, or sending information to the wrong parties.
For technical work, a sensible practice is to give agents a repository copy, anonymized data, and limited permissions. For administrative tasks, agents can first create drafts of emails or change lists without directly sending or applying them.
New Issues: Who Is Responsible?
When AI only provides answers, humans usually remain the final executors. When agents begin to take action, the lines of responsibility become more complicated. Is the fault with the model, the workflow creator, the data owner, or the person granting approval?
According to editorial analysis, this question cannot be resolved simply by adding a label “created by AI.” Systems need to leave an auditable trail: initial instructions, data sources, tools called, changes made, and decisions requiring approval.
Therefore, evaluating agents should not stop at the question “is the answer correct?”. Testing should also include the following:
- Is the agent using the correct data sources?
- Does the agent stop when permissions are insufficient?
- Can the agent recover after a tool fails?
- Does the agent avoid sending or deleting something without approval?
- Are all its steps auditable?
What It Means for Us
For regular users, this development means AI will increasingly act as a workflow executor, not just a question-answering companion. However, not all tasks are suitable to be fully delegated to agents.
Start with repetitive tasks that have clear boundaries and are easy to verify. For example, converting forms into draft reports, categorizing support tickets, summarizing meetings, or checking document completeness. Avoid granting full access for payments, data deletions, account changes, or sending important messages at the initial stage.
Use a three-tier permission model:
- Read: the agent should only view the necessary data.
- Prepare: the agent can create drafts, recommendations, or temporary changes.
- Execute: the agent can apply actions once rules and approvals are met.
This model is indeed slower than granting full access. However, a little added friction is much cheaper than fixing incorrect transactions, reports, or configurations.
What Can Be Done Now
Before using an AI agent, write a simple one-page rule set. Include the agent's objectives, data that can be read, tools that can be used, prohibited actions, and conditions that require escalation to humans.
After that, test the agent with normal cases and deliberately confusing cases. Provide empty data, conflicting instructions, and revoked access mid-process. Observe whether the agent stops safely or continues to guess.
The fact that AI providers are racing to provide APIs, connectors, sandboxes, and evaluations shows a clear direction for the industry: the future of AI is not solely determined by the model's ability to generate text. The real value will emerge when agents can operate in real-world environments without losing boundaries, trails, and human control.
Sources & Further Reading
- Introducing the Agents API - OpenAI
- Google Cloud introduces the Gemini agent
- Anthropic acquires Stainless
- The next evolution of the Agents SDK - OpenAI
– Rio Yotto @rioyotto